Security thatticks boxesjust works.
Fractional CISO, transformation, architecture and board advisory for regulated businesses. Built to enable the business, not to appease the audit.
What has changed for you?
- A new mandateI have just taken the seat, and the board wants to know where we really stand.
- New regulationA regulation now applies to us, and nobody can tell me what that means or by when.
- New technology, new strategyWe are moving to the cloud, or adopting AI, and security should not be the thing that stops it.
- After a breachWe have had an incident, or a near miss, and I need to be believed again.
- A dealWe are buying, selling or being bought, and diligence will ask what we cannot yet answer.
- A customer or insurer asksA customer, a tender or an insurer wants assurance, and we keep losing time to the paperwork.
Fractional CISO
Senior security leadership, embedded in your business, translating cyber into decisions your board can actually make.
Transformation
DORA, NIS2, resilience: delivered as a better way of operating, so your people see what security does for them, not what it stops.
Security architecture
First-principles design that fits how your firm actually runs. If a control needs a 40-page explanation, it's the wrong control.
NED and board advisory
Independent cyber counsel in the boardroom: plain answers to the questions regulators expect your board to ask.
Security training and awareness
Plain-English awareness that changes what people do: role-specific sessions, drills that coach, and board briefings without the jargon.



Assess
Capture the current state, such as a framework self-assessment, and see what you have got.
Usually lives in
A spreadsheet or a GRC toolDecide
Triage the findings and make the scoping calls. The decisions and the reasons are recorded.
Usually lives in
Email threads and meeting minutesDeliver
Plan the work: the Gantt, the steps, the risks and the benefits.
Usually lives in
A project toolSteer
See the budget against the spend, and what is drifting, before the board does.
Usually lives in
A finance spreadsheetProve
Produce the board pack, with evidence behind every line.
Usually lives in
Slides, assembled by hand
Ready to think outside it?
An engagement starts with a conversation: you describe the problem the way you would to a colleague. No charge, no deck, and if we are the wrong firm for it, that is where we say so.
Where we stand.
1 to 4 of 10
 DORA isn't your problem. Your operating model is.
 Why is the King obsessed with cyber?
 The 40-page control document is a confession.
 The defender's OODA loop is broken (and what to do about it).
 Stop showing your board heat maps.
 Mental health at the security coalface.
 Orchestrating AI agents.
 A threat-led cyber security strategy for 2025.
 Post-quantum cryptography: what is it and why should I care?
 Cyber risk and digital public services.
Nothing under that topic yet.
Frameworks we advise on.
Regulated, newly regulated or about to be. We advise on these; we do not claim them. Outside The Box Consulting does not currently hold ISO 27001 or Cyber Essentials.
- Regulation and resilience
- Assurance and standards
- Architecture and method
Who you'd actually be working with.
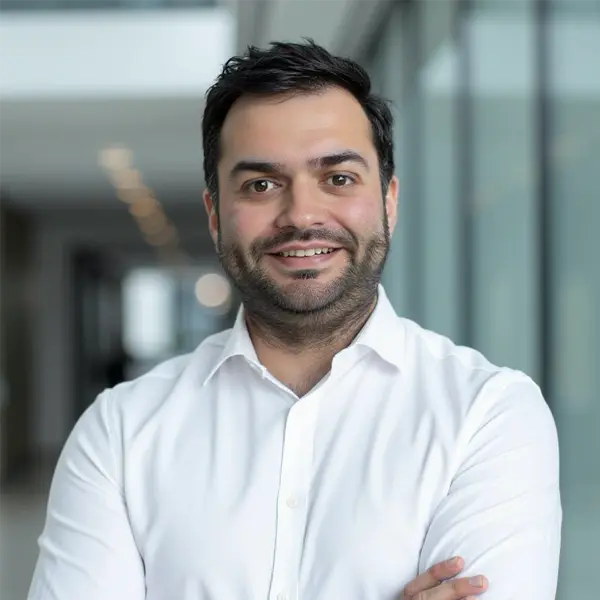
Chris Whitehead
Founder
A security architect who came up through PwC and BAE Systems: nearly twenty years designing and assuring security across financial services, energy and government, in IT and in the operational technology that runs physical things. Through the practice he has served as interim Head of Information Security at a UK central government department, and he has assessed a government agency's OT network as a Code of Connection Assessor. He sits on the two British Standards committees that maintain ISO 27001.
Fellow of BCS, Chartered IT Professional, Chartered Security Architect (SABSA), CISSP, CCSP, CRISC, MSc Information Security (Royal Holloway).
Larger engagements draw on associates and partners, alongside him.
The person you meet is the person you get.